Watch your endpoints for active exploitation in real time.
Vulnerabilities tell you what could happen. Endpoint telemetry tells you what is happening. AegisVMP puts both on the same asset.
Endpoint event monitoring
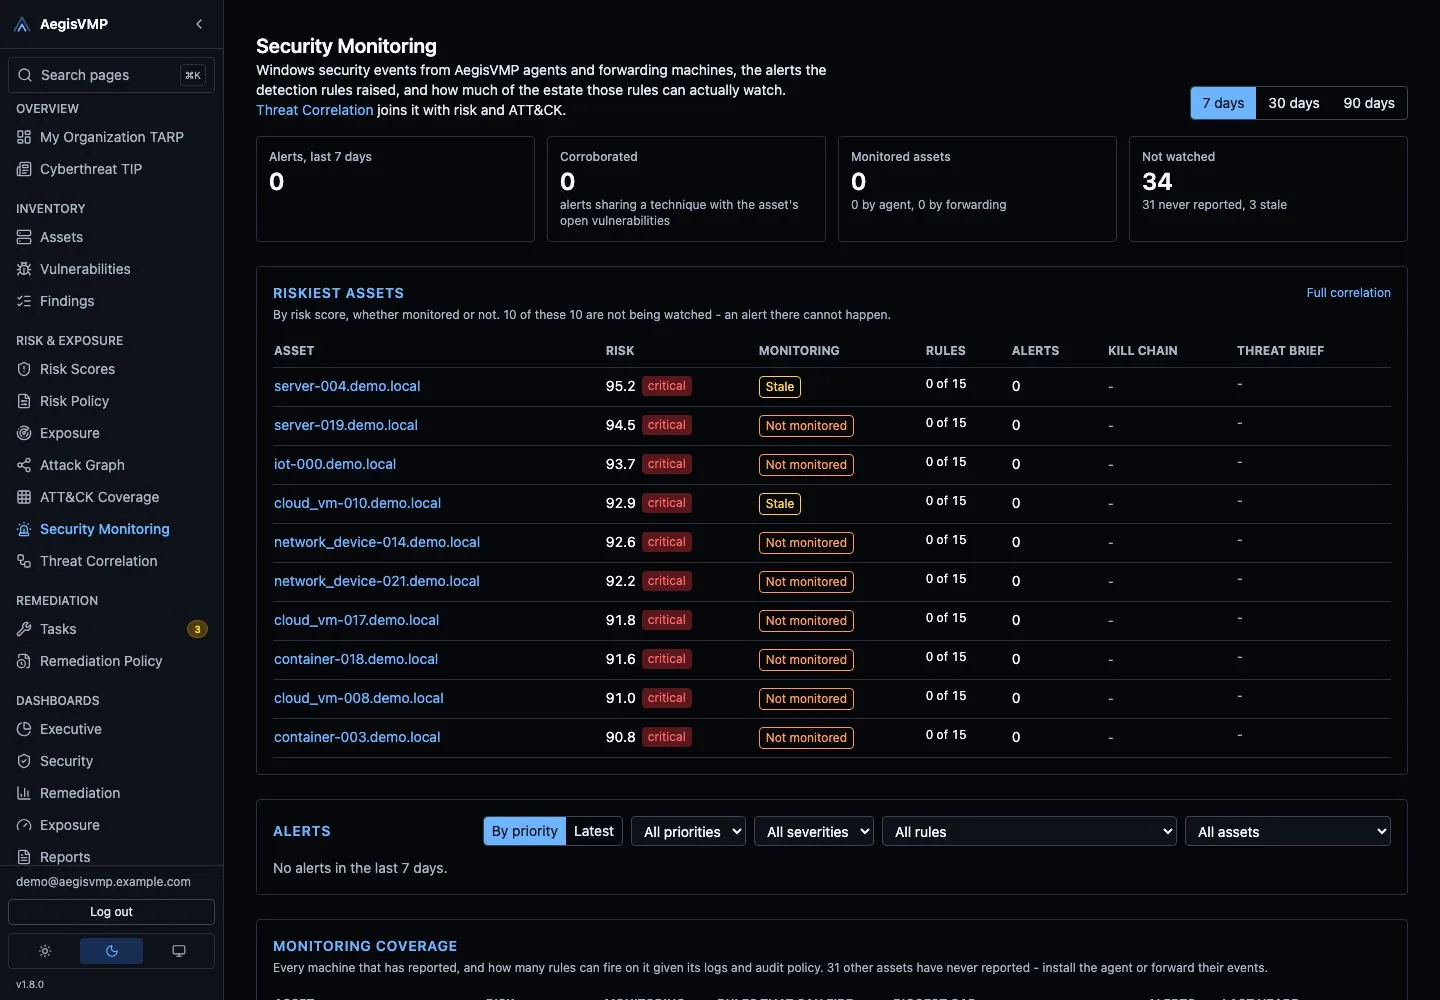
Endpoint Agents watch Windows event logs: sign-ins, failed logons, account and group changes, new services and cleared logs.
15 ATT&CK-mapped detection rules
Each detection rule is mapped to a MITRE ATT&CK technique, so an alert says which attacker behaviour it represents.
Corroboration engine
Active alerts are linked to the open vulnerabilities on the same asset. Matches are flagged Corroborated for analyst action.
Blind-spot tracking
See which assets are monitored and which are not, and whether monitoring is feasible for each one.
Forensic compromise checks
Check an asset's event history for signs of compromise around the time a vulnerability became known.
What is watched, and what is not
The Security Monitoring page lists monitored machines, recent alerts by ATT&CK technique and the blind spots where no telemetry is arriving.
Alerts meet vulnerabilities
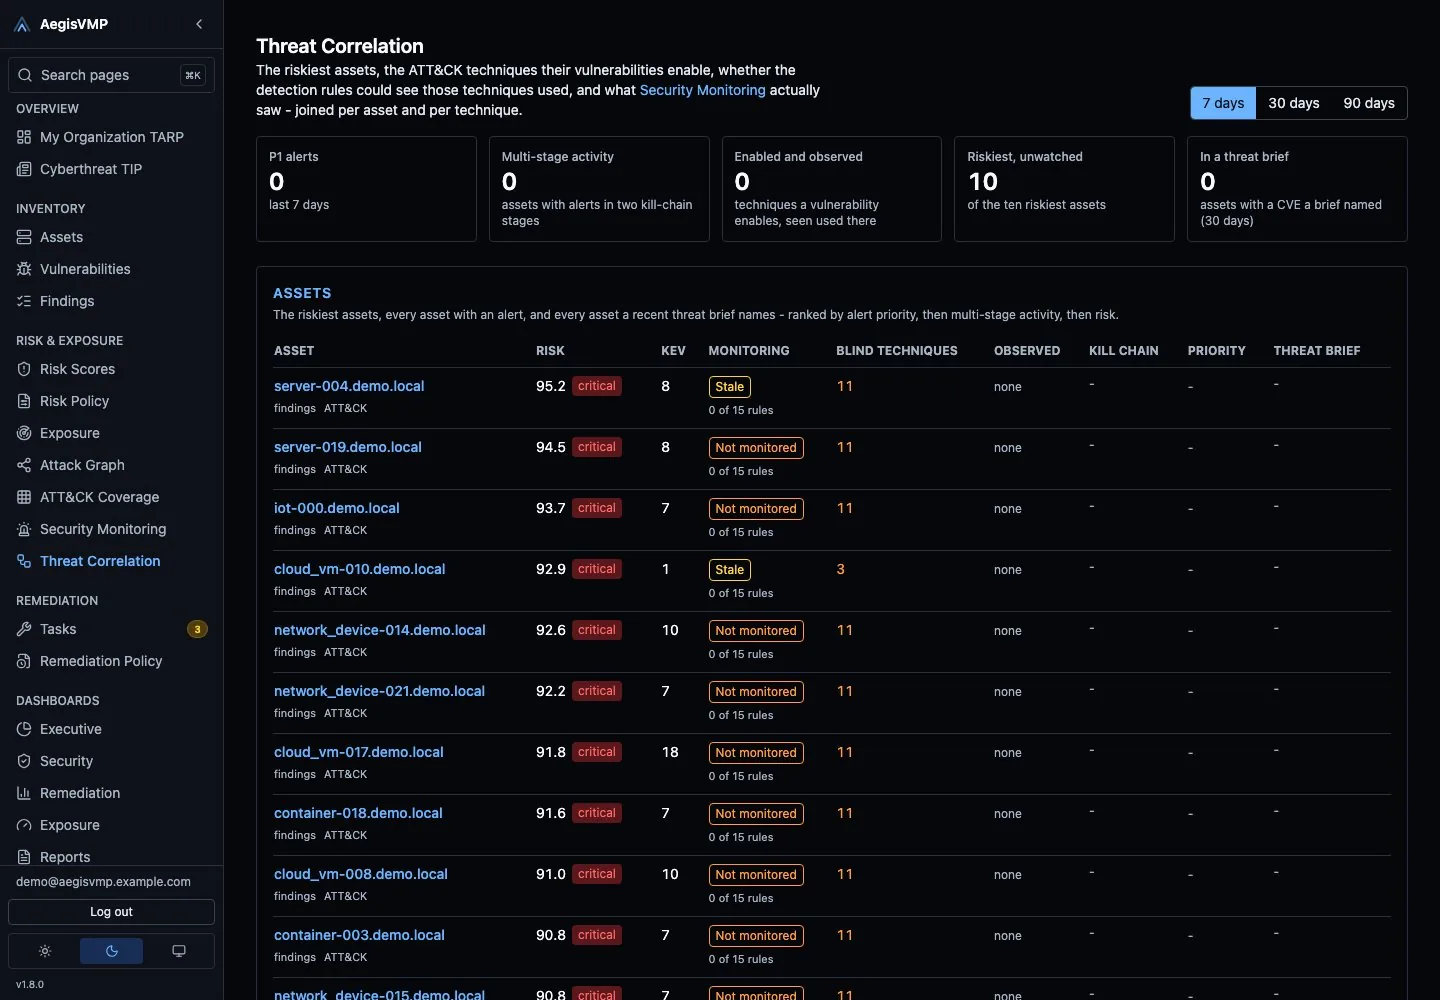
A detection on a machine with a matching open vulnerability is flagged Corroborated. The flag prompts an analyst; it does not change the priority score by itself.
Corroborated signal
When telemetry agrees with a vulnerability, the finding is flagged.
When endpoint telemetry agrees with an open vulnerability on the same asset, AegisVMP flags the finding as Corroborated so an analyst can act on it. The flag does not change the priority score by itself.
- Independent sources agree
- Flagged Corroborated for analyst action
- The reasoning stays attached to the finding
See monitoring on your own endpoints
Request a walkthrough of AegisVMP and see how unified intelligence changes what your team works on first.