Beyond Vulnerabilities
Context tells you how dangerous a vulnerability is to your organization.
AegisVMP discovers your assets, works out which known vulnerabilities really apply to them, and ranks them by danger using threat intelligence, exposure, attack paths, and endpoint telemetry.
- NVD · CISA KEV · EPSS
- Asset discovery
- Endpoint telemetry
- Exposure
- Attack paths
- AI
Security teams are not short on data. They are short on meaning.
Vulnerability lists grow every week. Severity ratings describe the flaw, not the organization. The context that would make prioritization obvious is scattered across tools that never meet.
Fragmented security data
Assets, vulnerabilities, signals and threat intelligence live in separate tools that rarely agree.
Volume without meaning
Long vulnerability lists grow faster than teams can act, and counts do not describe danger.
Severity is not risk
A high severity score says nothing about whether a specific asset is exposed or reachable.
Missing context
Without asset criticality, exposure and business context, prioritization becomes guesswork.
Unseen relationships
Lists rarely show which vulnerable systems an attacker can actually reach from the internet.
Disconnected remediation
Decisions made in one system are executed in another, so progress is hard to see and verify.
Discover → Reassess
Seven connected stages, not seven disconnected tools. Each stage carries its context forward, and the loop closes so posture keeps up with a changing environment.
Many sources in. One coherent picture out.
AegisVMP discovers assets, matches their software against NVD, CISA KEV and EPSS, adds exposure and endpoint telemetry, then turns that model into prioritized, explainable outcomes.
Eight capabilities that work as one system
Each capability is useful alone. Together they compound, because every one of them reads and writes the same unified context.
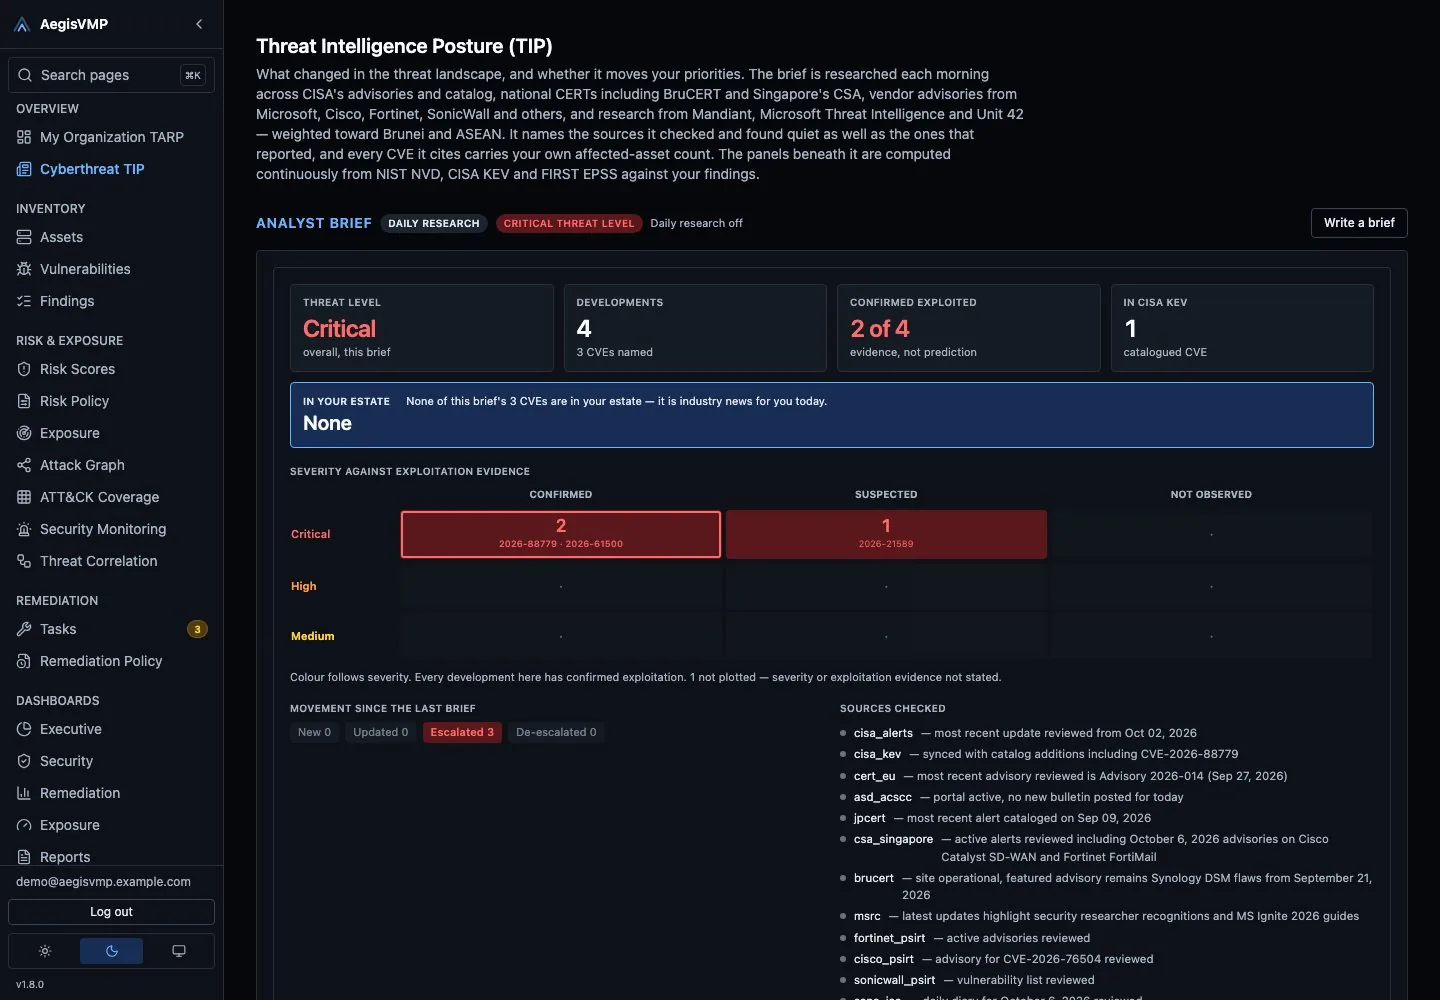
A daily threat brief, matched to your own assets
Every day AegisVMP's AI researches the current threat landscape and correlates it against your organization's assets and open CVEs, so you see which headlines actually touch you.
Threat-Aware Risk Posture, on one screen
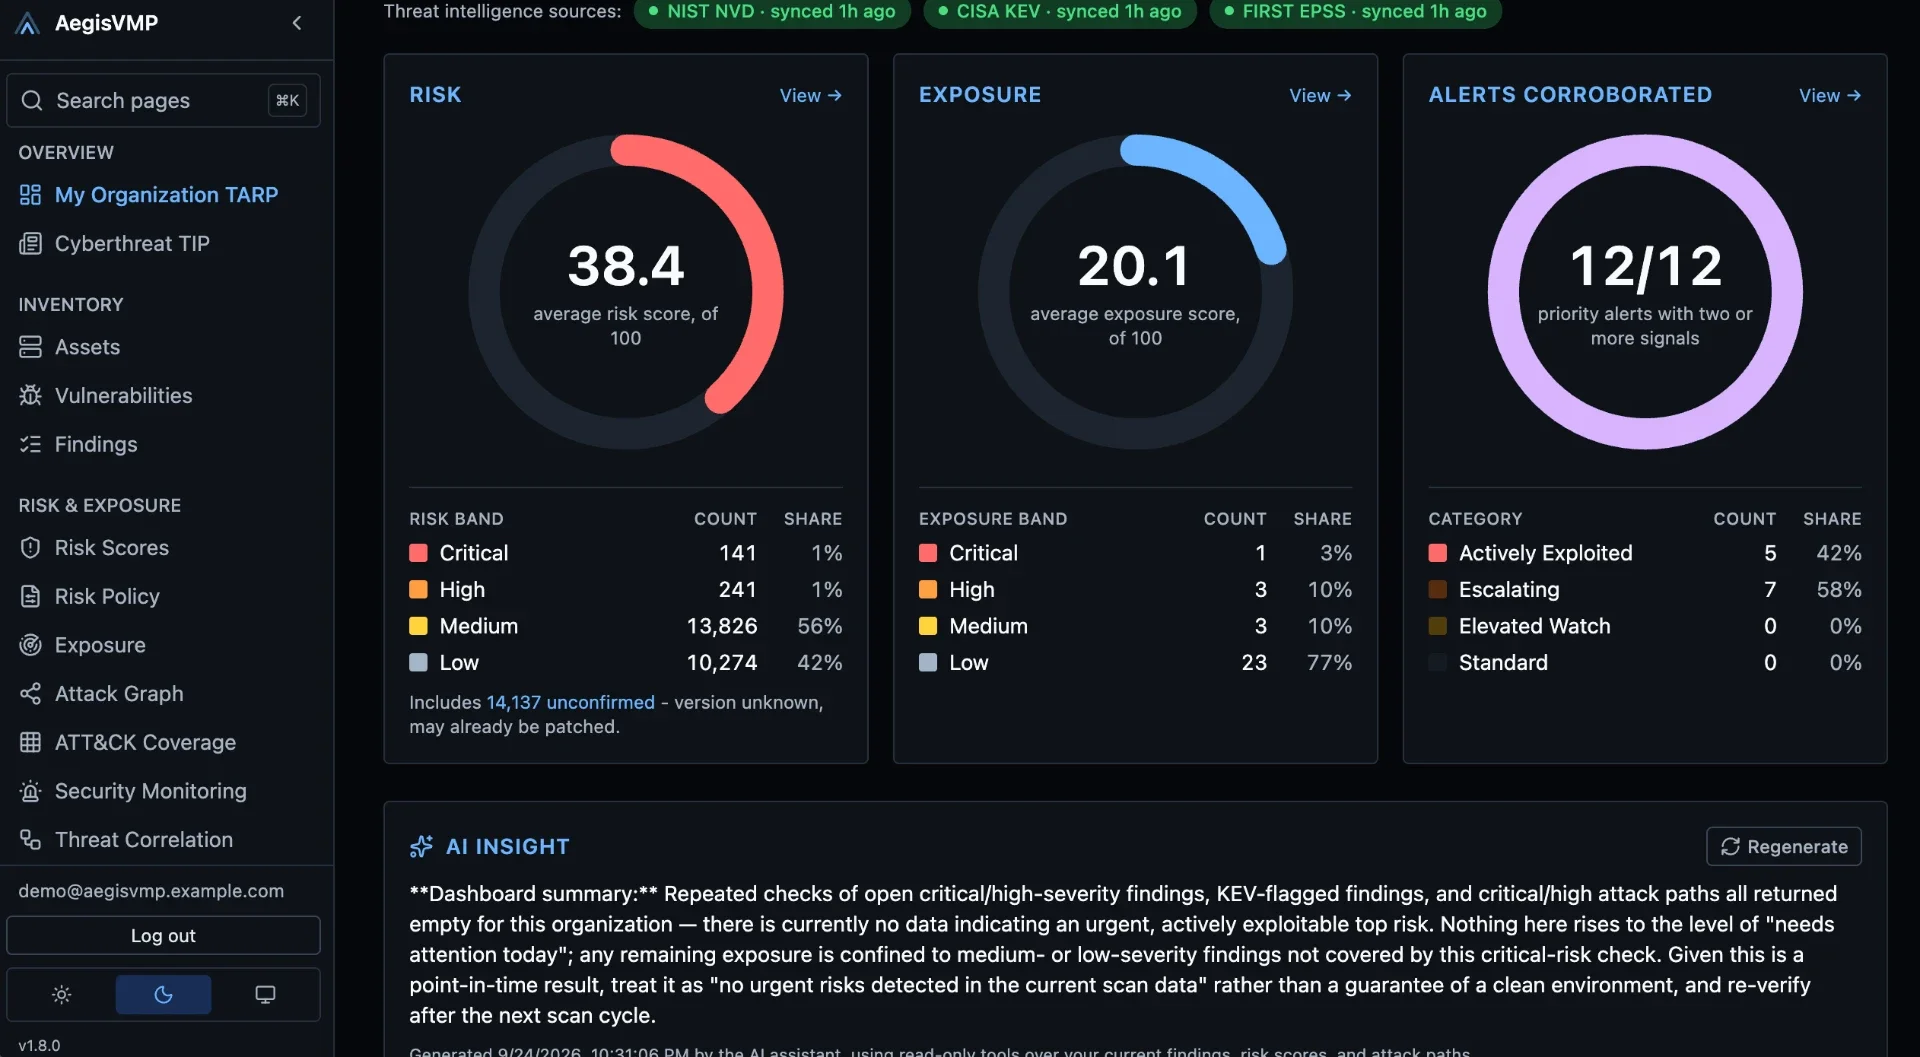
TARP leads with average risk, average exposure and corroborated alerts, broken down by band and correlated against live CISA KEV and FIRST EPSS data — not with a raw count of open findings.
Confidence comes from agreement
When endpoint telemetry agrees with a vulnerability on the same asset, the finding is flagged Corroborated for analyst action.
Context tells you how dangerous a vulnerability is to your organization
Severity is a property of the vulnerability. Danger is a property of your environment. AegisVMP scores the second one.
From the internet to the vulnerable asset
AegisVMP maps the routes from the internet to exposed assets and the vulnerabilities on them, scores each route and maps it to ATT&CK tactics.
Explanations your whole organization can read
AI turns layered technical context into a narrative: what the finding is, why it ranks where it does, and what could reduce the risk. Every output is written for human review.
Prioritization only matters if the work moves
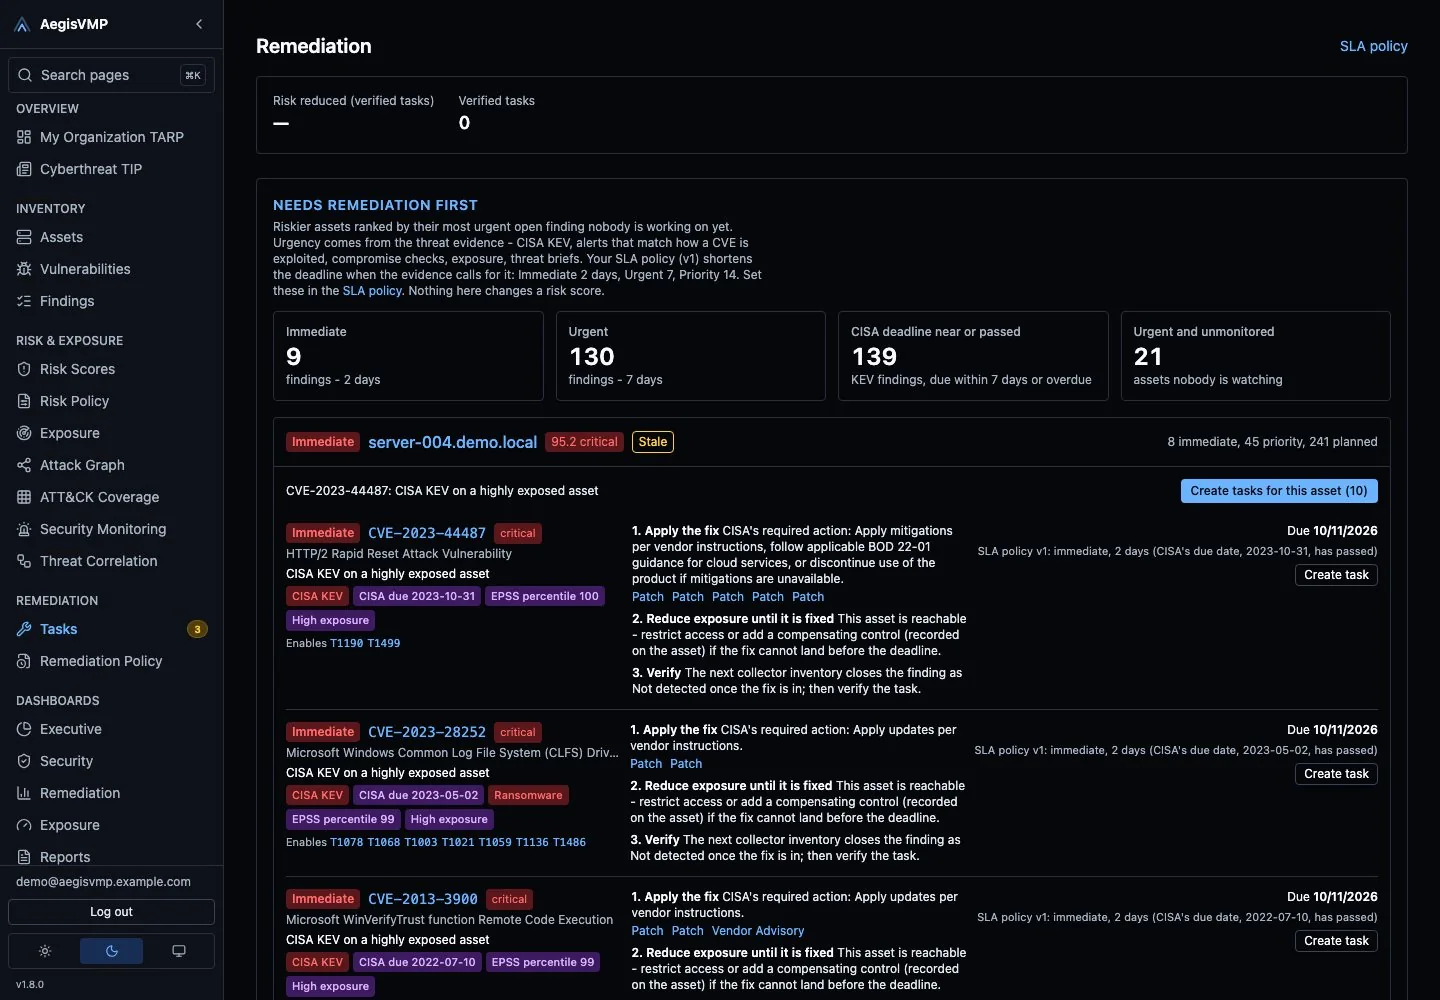
Prioritized findings flow into structured workflows with ownership, status and visible progress, so the decision made in the platform is the work that actually gets done.
One story, told at every altitude
Because analysts and leadership read the same underlying model, executive views summarize the same context that drives day-to-day remediation decisions.
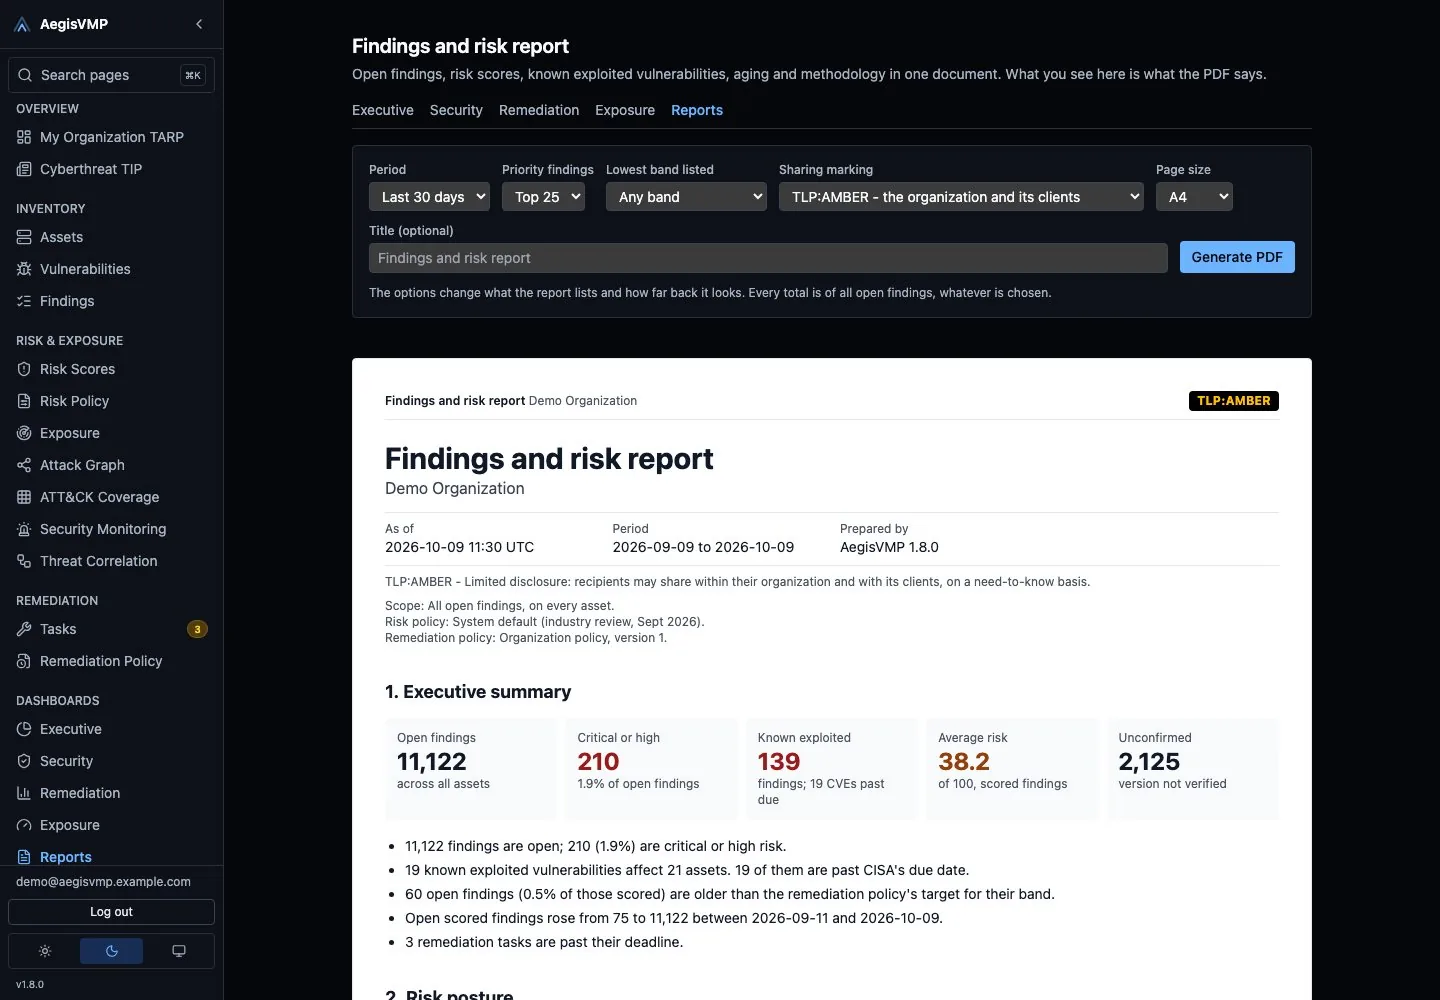
Built to sit on top of what you already run
AegisVMP is designed to consume data from the categories of systems that already exist in a security program, and to hand prioritized work back to the places where it gets executed.
Public vulnerability catalogues
NIST NVD, CISA KEV and FIRST EPSS, synchronized automatically.
Identity and cloud
Microsoft Entra ID devices and Azure virtual machines.
Asset discovery
Tenable.io asset discovery, CSV and CycloneDX imports.
Collectors and agents
AegisVMP Site Collectors and Endpoint Agents.
Ticketing
Jira, ServiceNow and GitHub Issues for remediation tasks.
Notifications
Slack and custom webhooks.
Named integrations available in AegisVMP 1.8.0.
Structured for how large organizations actually operate
Access, separation, auditability and a consistent data model are part of the platform's design rather than additions on top of it.
Role-based access
Granular permissions grouped into roles, so people see what their job requires.
Tenant isolation
Each organization's data is separated in the database with row-level security.
Immutable audit log
Sign-ins, privilege changes and report downloads are recorded and cannot be edited.
Operator Console
A separate realm for provisioning organizations, with no view of customer data.
See context in action
Request a walkthrough of AegisVMP and see how unified intelligence changes what your team works on first.